
Audit log
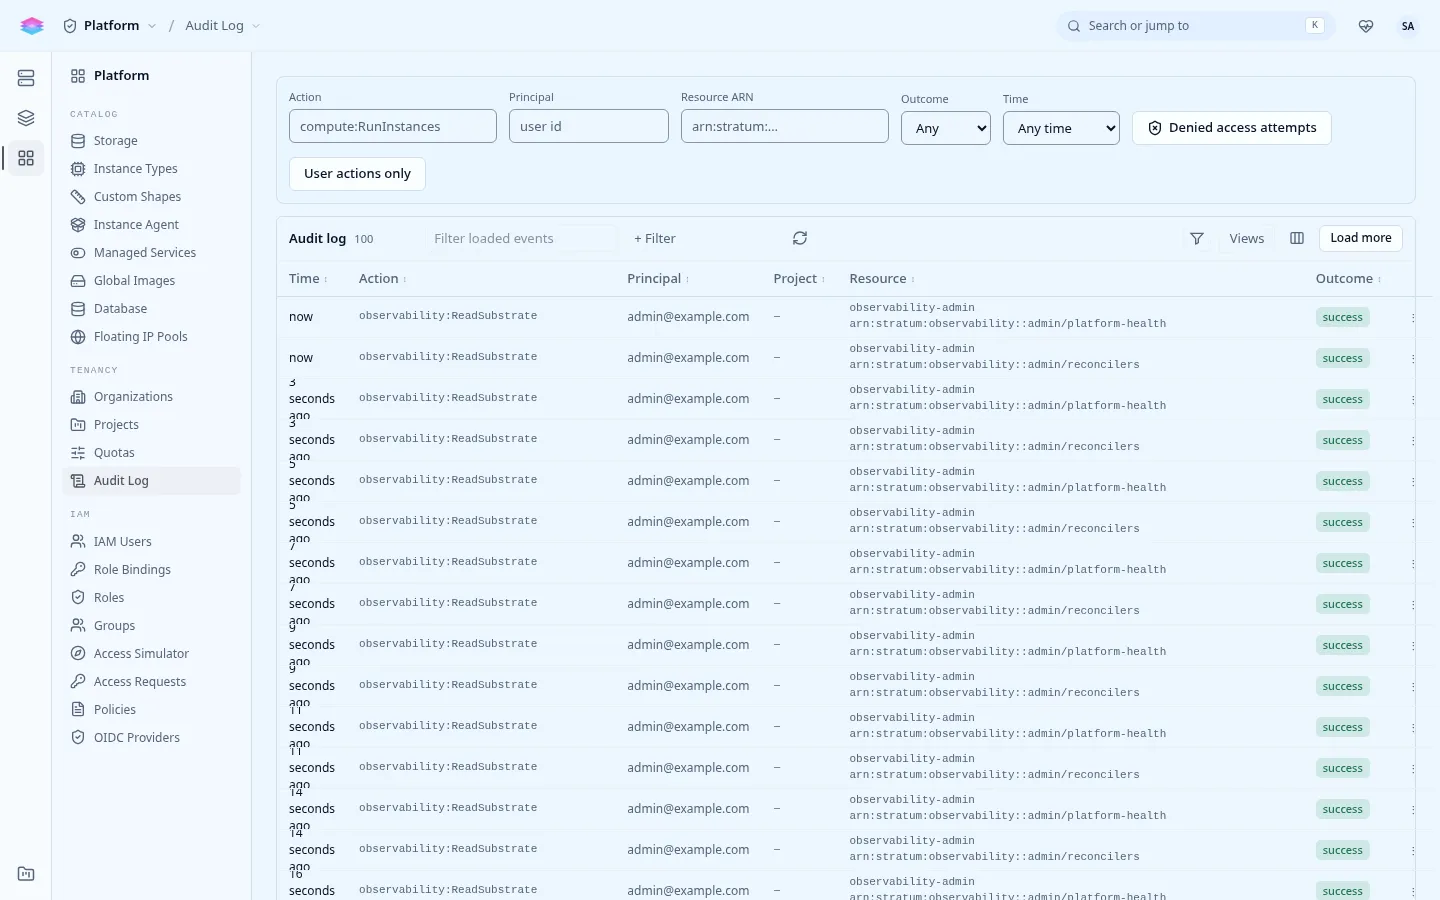
Every call that changes something, and every refused one, is written to the audit log with who made it, from where, on what, and the outcome. The log is a hash chain: each event carries the hash of the one before it, so an edited or deleted event breaks the chain.
Console: Admin › Platform › Tenancy › Audit Log for the whole cloud; each project’s Audit Log for its own events.
stratumctl audit query # newest first, the whole cloudstratumctl audit query --project p-web --limit 200stratumctl audit query --oldest --limit 20stratumctl audit verify # check the whole chainstratumctl audit verify --from 2026-10-01T00:00:00Z --to 2026-10-13T00:00:00Zverify exits non-zero when the chain is broken, and says where.
What else is audited, besides API calls: sign-ins and failed sign-ins, password and MFA changes, upgrades and each state they pass through, shutdowns, sessions into instances, agent refreshes, and changes to settings such as the operator webhook (the event records the change, never the URL).